SOC 2
Get ready for your SOC 2 audit.
SOC 2 without the headache. LakeRidge guides your assessment against the Trust Services Criteria, plans every fix, and keeps your policies and evidence ready for your auditor.
Find out how LakeRidge can help your team.

Trusted by defense, manufacturing, research, and IT teams at small businesses and enterprises alike. Compliance since 2014.

Quick and simple
Here’s how we get you ready for your SOC 2 audit.
Security is part of every SOC 2 audit. Add Availability, Confidentiality, Processing Integrity, or Privacy when they are in scope for yours.
-
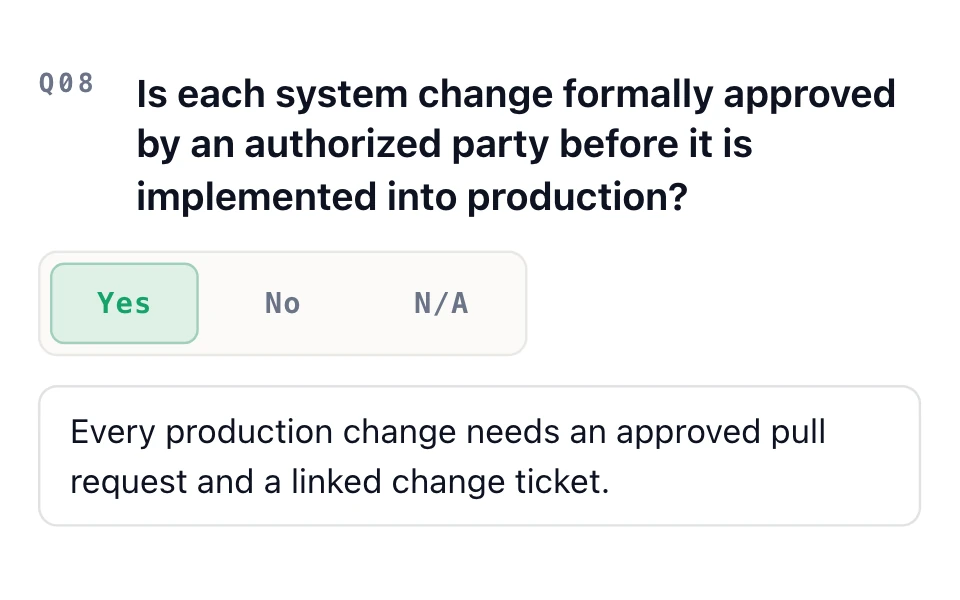
Easy yes-or-no questions
Assess
Answer guided yes-or-no questions for each of the Trust Services Criteria in scope. LakeRidge shows which criteria you meet and where you have gaps, so you know where you stand before your auditor does. Our team of certified cybersecurity professionals can perform the assessment with you.
-
Driven by automation
Plan
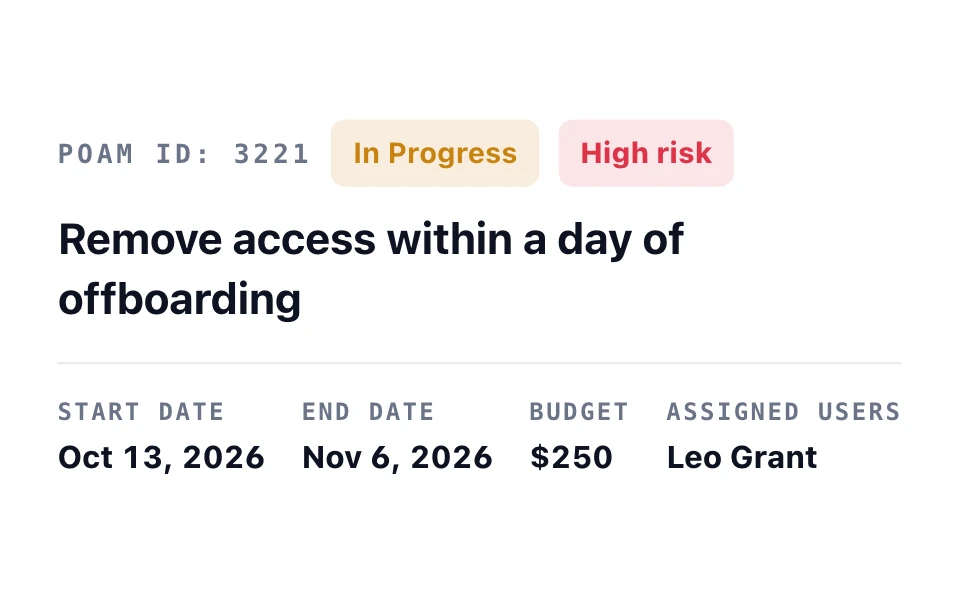
Every gap becomes a risk-rated task in your remediation plan, with an owner, dates, and a budget, so your team knows exactly what to fix before the audit. Our certified professionals can help you implement the fixes.
-
Get a head start
Document
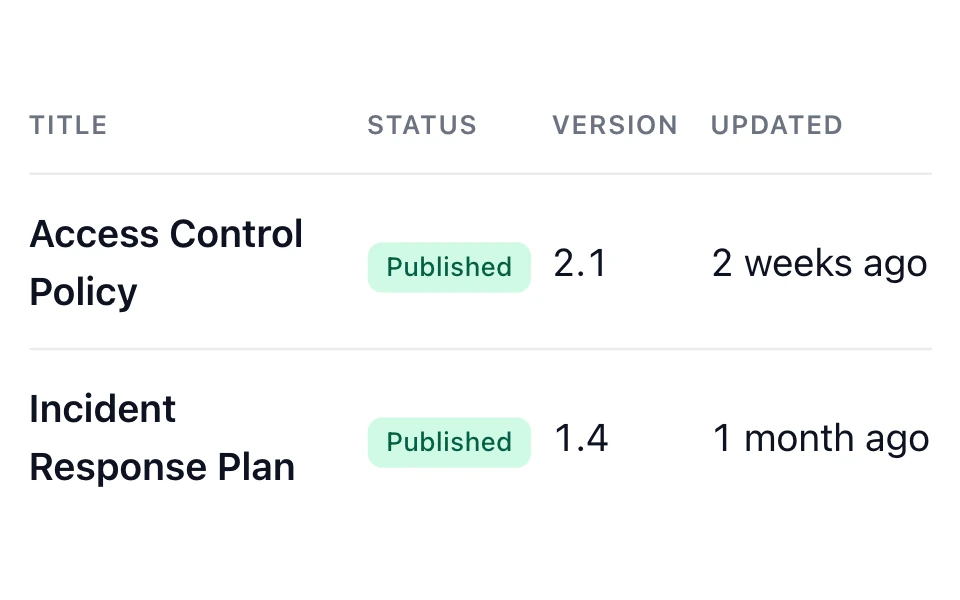
Start from more than 50 policy and procedure templates, including your information security policy, access control policy, incident response plan, and vendor management policy. Each one is customizable and versioned in one place. Draft your system description for your auditor alongside them.
-
Stay on top, stay ahead
Maintain
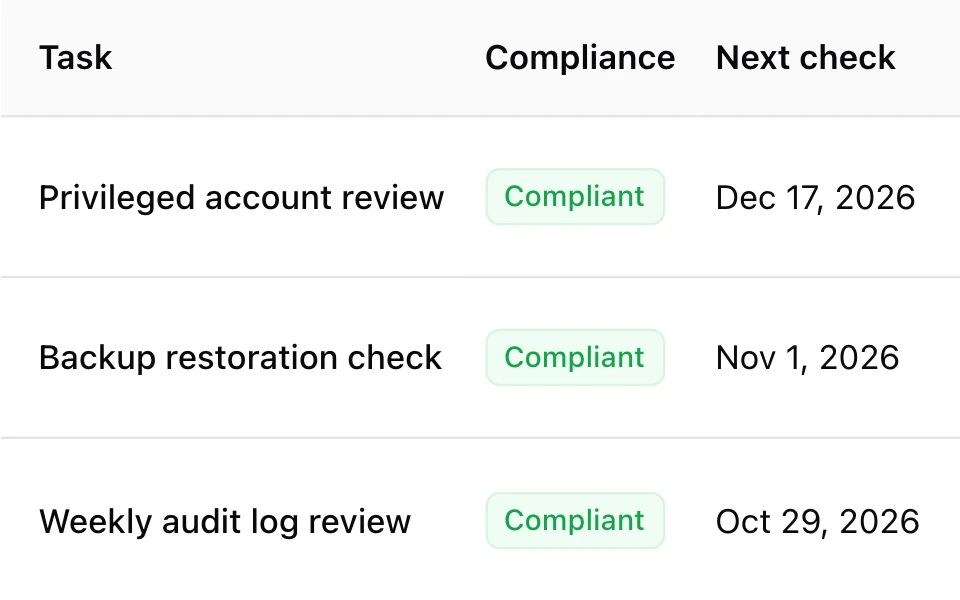
A SOC 2 Type II audit looks at how your controls operate over time. Recurring reviews remind your team when each check is due, and evidence attaches to the exact criterion it proves. When you are ready, your CPA firm performs the audit.
One platform, three use cases
SOC 2 for you, your clients, and your suppliers.
-
For your business
Become compliant and stay compliant. Everything on this page is how we get you there.
-
For your clients
Provide clients with compliance services using our GRC app with your own branding.
Provide compliance -
For your supply chain
Verify, monitor, and support supplier/subcontractor compliance.
Verify compliance
Trusted worldwide
What our customers are saying about us.
-
“This app put into perspective and laid out exactly what we needed to do to become compliant.”
 Christopher DavisIT Manager, InnovaPrep
-
“App is very easy to use and very straight forward. I have seen many apps in searching for a company to work with, the LakeRidge app was by far easier to use.”
 Chris ClarkVice President and COO, EOS-AV Corp
-
“In a growing complex field of cyber security, it is very difficult to find a simple flashlight for small companies to find their way through the dark labyrinth. The App is very well organized and most helpful in guiding our way forward.”
 Will KohnenPresident, Hydrospace Group

See LakeRidge in action.
Talk with our team about your framework, your gaps, and the right plan.
Get a demo